
IT operations out of the box, and any agent you need beyond it
Our predefined agents already run IT operations on the platform: they watch, investigate and report, and change only what you have approved. The runtime runs any agent, so the same platform carries the rest of your work.
SRE troubleshooting
Watches your observability events, troubleshoots what fires and takes the proactive step you approved, before anyone is paged.
Observability investigation
Investigates an incident over a fixed window and reports what happened, with evidence behind every claim.
Agent log inspection
Reads the logs your agents leave behind and flags what failed and what looks wrong.
Reporting
Turns the data you already collect into the report someone used to compile by hand, on a schedule.
Agentic SDLC
Agents that plan, write, review and test code, each run in its own sandbox with only the repositories it needs.
Business operations
Agents that work through tickets, documents and approvals in the systems your teams already use.
Workflow automation
Multi-step workflows that hand work between agents and people, with every model and tool call recorded.
Your own agents
An agent you built and maintain, on any framework, runs here the same way as ours.
From the catalogue to a running agent, on your cluster
Choose an agent from the catalogue, such as OpenClaw, Hermes Agent or NanoClaw, or one we build with you. Or bring an agent you have developed and maintain yourself: we are the agent runtime it runs on.
Give it the tools and data its job needs, and nothing more. Its access lasts only as long as the task.
It runs on your own nodes, in its own sandbox, and every model and tool call is recorded.
Safe by default, without slowing anyone down
It only touches what you allow
An agent gets the minimum access its task needs, only for as long as it needs it, and asks for more through a process you approve. One key for one door, valid on its shift.
It works in its own sandbox
Code and tool calls run in a sandbox on your own nodes, with no view of the cluster and network access only to endpoints you allow. The skills you attach to an agent are mounted in its sandbox by default, with no work needed in the agent.
It cannot be talked into things
Log lines, documents and web pages an agent reads are treated as data, never as instructions. An attacker who writes “delete the database” into a log line gets a log line.
One place to watch it and stop it
Every model call and tool call goes through one gateway: budgets per agent and per team, a switch between local and hosted models without touching the agent, and one place to cut it off.
Public skill registries are already a target. Snyk scanned 3,984 public agent skills in February 2026: 36.8% had at least one security issue, 13.4% a critical one, and 76 malicious payloads were confirmed by human review. Koi Security audited all 2,857 skills on ClawHub the same month and found 341 malicious ones, 335 of them from a single campaign delivering a macOS credential stealer.
Every agent reports the same signals
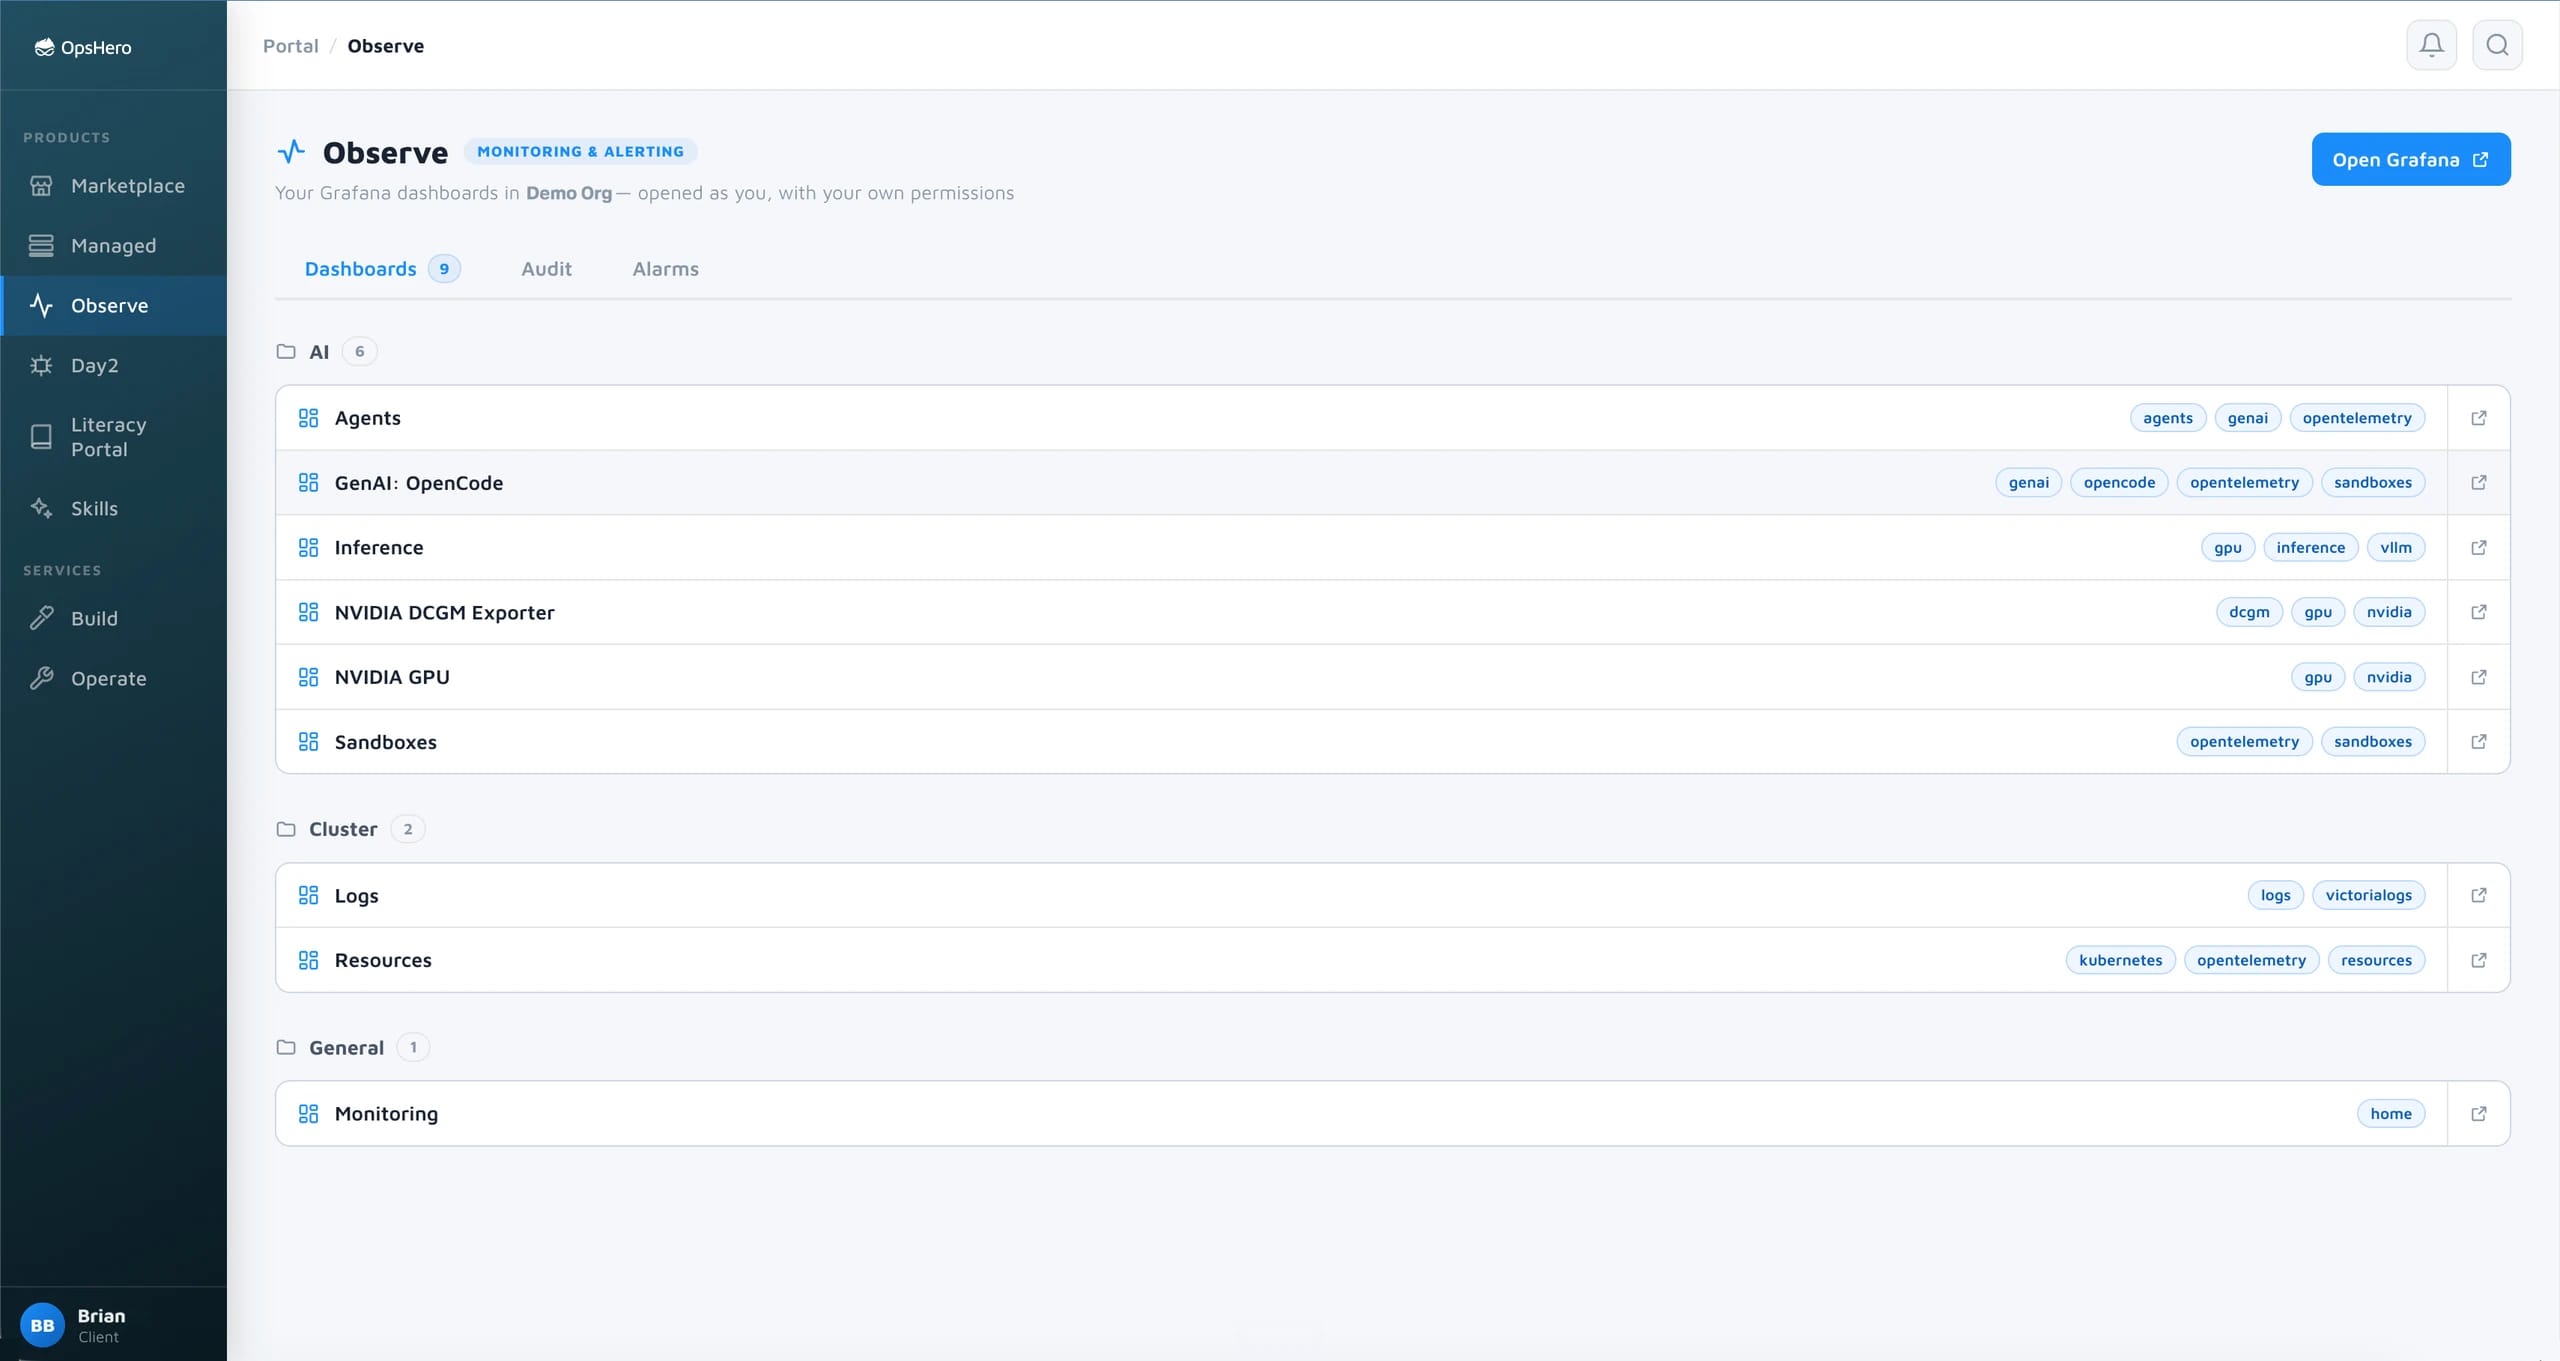
Every agent reports the same signals: which model it called, which tools and MCP servers it used, how many tokens, and what it cost. They sit next to your infrastructure metrics, not in a separate product. Observability →
Runs the agents you already know, and the ones you build with us
Agents from the catalogue
OpenClaw, Hermes Agent, NanoClaw and OpenShell run on the platform today, deployed from the catalogue to your own nodes.
 OpenClaw
 Hermes Agent
 NanoClaw
 OpenShell
Agents built with you
Any agentic framework is compatible, from Google ADK to Microsoft Agent Framework to LangChain. Nothing in an agent depends on a runtime library that only works in one cloud.
- Google ADK
- Microsoft Agent Framework
- LangChain
The ones people actually ask
Can it run on our own machines only?
Yes. Agents run as workloads on your nodes. Model calls can stay local if you run models locally.
What stops an agent from doing damage?
Its permissions, its sandbox and its network policy, in that order. Not its instructions, because those can be overridden by what it reads.
Which models can agents use?
Any model behind the gateway: local open-weight models or the hosted APIs you already pay for.
Do you build the agent, or do we?
Either. Most first agents are built with us, in an engagement.
Is a chatbot or a coding assistant an agent?
Not on its own. A chatbot answers; an agent acts on what the model concludes. When a coding assistant runs unattended, on a schedule, with its own identity, it becomes one, and then everything above applies. We also run no-code and low-code agents built on top of Claude Code, and they are treated exactly like an agent built in code.
What does it cost?
You pay for the cluster control plane, and there is no limit on how many agents you run. If you would rather not build them yourself, we can also build and maintain the agents for you.
Bring one process. Leave with a design for the agent that runs it.
- Which step of your process is actually an agent, and which is a script
- What it would need access to, and what it would not
- Where it would run and what it would cost to find out